SEC Consult Vulnerability Lab Security Advisory < 20261023-0 >
=======================================================================
              title: Multiple Cross-Site Scripting Vulnerabilities
            product: VertiGIS WebOrderSystem (KundenManager, AuftragsManager)
 vulnerable version: <=7.0.8.6
      fixed version: unknown
         CVE number: CVE-2026-4950, CVE-2026-4951, CVE-2026-4952
             impact: medium/high
           homepage:https://www.vertigis.com/
              found: 2025-01-14
                 by: Kai Zimmermann (Office Frankfurt)
                     SEC Consult Vulnerability Lab

                     An integrated part of SEC Consult, an Atos business
                     Europe | Asia

                     https://www.sec-consult.com

=======================================================================

Vendor description:
-------------------
"VertiGIS creates industry-leading technology that advances spatial visibility
into assets – across industries and across the globe. Our intuitive range of
use-case-based tools can help you solve complex business challenges, leverage
spatial data in new ways and build solutions that make a difference."

Source:https://www.vertigis.com/


Business recommendation:
------------------------
The vendor did not communicate a patch for the identified vulnerabilities in
VertiGIS "WebOrderSystem" and told us that "LM Explorer" will incorporate the
fixes. Version numbers were not provided nor when the fixes were implemented.

A workaround exists for CVE-2026-4952, which should be applied while no
official fix is available. Contact the vendor fur further information
regarding fixes or hardening measures.

SEC Consult highly recommends to perform a thorough security review of the
product
conducted by security professionals to identify and resolve potential further
security issues.


Vulnerability overview/description:
-----------------------------------
1) Stored Cross-Site Scripting in VertiGIS CustomerAdministration Portal
(CVE-2026-4950)
The VertiGIS CustomerAdministration portal (KundenManager) allows privileged
users to manage the employees (users) of defined companies (user groups). An
authenticated attacker with access to the CustomerAdministration portal can
insert malicious JavaScript code in a user's properties while editing the user.
The inserted code will be executed if other privileged users visit either the
user entry directly or the user overview of the specific user group.

2) Reflected Cross-Site Scripting in VertiGIS CustomerAdministration Portal
(CVE-2026-4951)
The VertiGIS CustomerAdministration portal (KundenManager) allows privileged
users to search for employees (users) across all defined companies (user
groups).
The search parameter "searchValue" can be embedded in the URL, so that if a
privileged user that is currently logged into the CustomerAdministration portal
visits that URL, the search will be performed. An unauthenticated attacker with
knowledge about the URL structure can craft a URL containing malicious
JavaScript code in the "searchValue" parameter. The inserted code will be
executed if the target privileged user visits the crafted URL while already
being logged into the CustomerAdministration portal.

3) Stored Cross-Site Scripting in VertiGIS OrderAdministration Portal
(CVE-2026-4952)
The VertiGIS "ASMobile" web interface, which is part of the software package
"GIS Portal", allows authenticated users to define a business reference. An
attacker can insert malicious JavaScript code inside the business reference.
Initially this issue affects the "ASMobile" web interface as what is considered
a "self-xss". However, when placing orders through the web interface, the
malicious
business reference will be included in the order details and will later be shown
in the OrderAdministration portal (AuftragsManager). The inserted JavaScript
code
will be executed if a high privileged user with access to the
OrderAdministration
portal visits the order that contains the attacker's malicious business
reference.


Proof of concept:
-----------------
1) Stored Cross-Site Scripting in VertiGIS CustomerAdministration Portal
(CVE-2026-4950)
When editing an existing user of a user group through the CustomerAdministration
portal, the following request, including malicious JavaScript code in the
"secondName" parameter, can be sent when saving the changes:

--------------------------------------------------------------------------------
[ PoC removed ]
--------------------------------------------------------------------------------

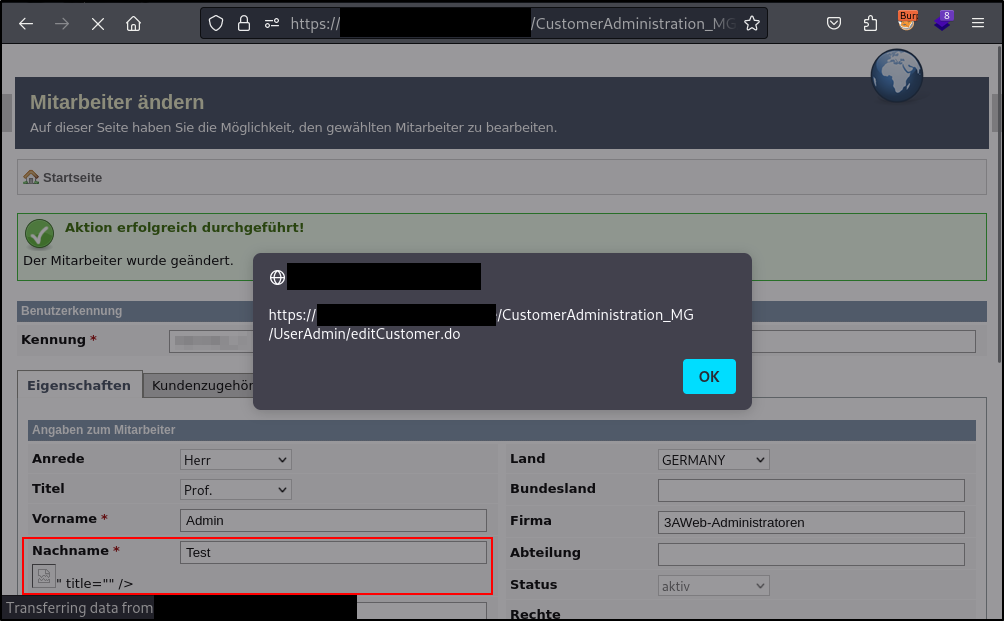
After saving the changes, the JavaScript code will be executed immediately after
the editing page, as can be seen in figure 1 below:

[01_stored_xss_01.png]

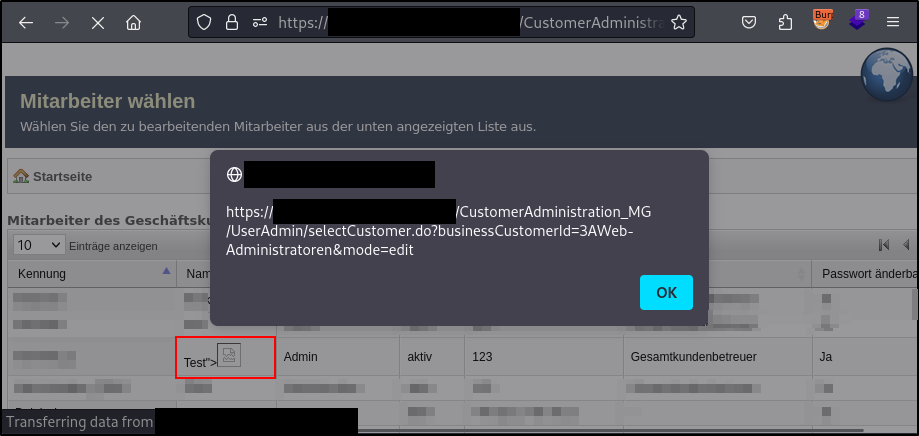
Figure 2 below shows that the JavaScript code will also be executed when a user
visits the user overview of the edited user's user group:

[02_stored_xss_02.png]


2) Reflected Cross-Site Scripting in VertiGIS CustomerAdministration Portal
(CVE-2026-4951)
An unauthenticated attacker with knowledge about the CustomerAdministration
portal's
URL structure can craft the following URL, which contains malicious JavaScript
code
in the "searchValue" parameter:

--------------------------------------------------------------------------------
[ PoC removed ]
--------------------------------------------------------------------------------

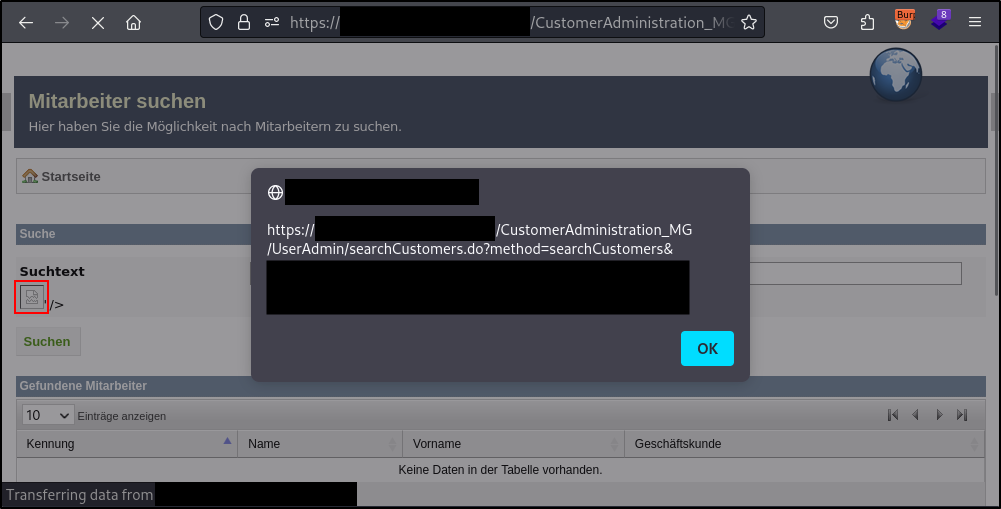
When a privileged user, who is currently logged into the CustomerAdministration
portal, visits the crafted URL, the included JavaScript code will be executed,
as
can be seen in figure 3 below:

[03_reflected_xss.png]

Potential further impacts may arise from the fact that administrative users can
change other user's (including other administrators) passwords without
specifying
the old password. An attacker may be able to craft a URL loading a remote script
that performs a password reset, allowing to either take over specific accounts
or lock out other users entirely from the application.


3) Stored Cross-Site Scripting in VertiGIS OrderAdministration Portal
(CVE-2026-4952)
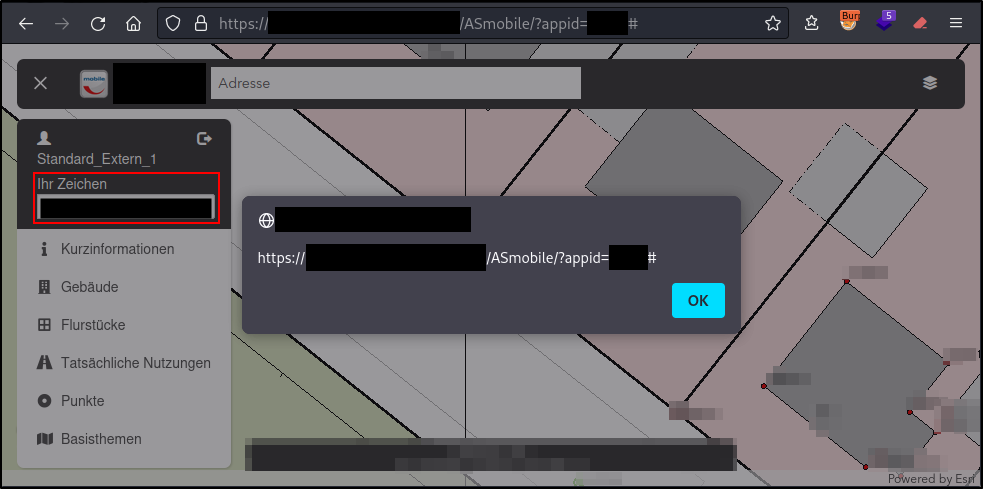
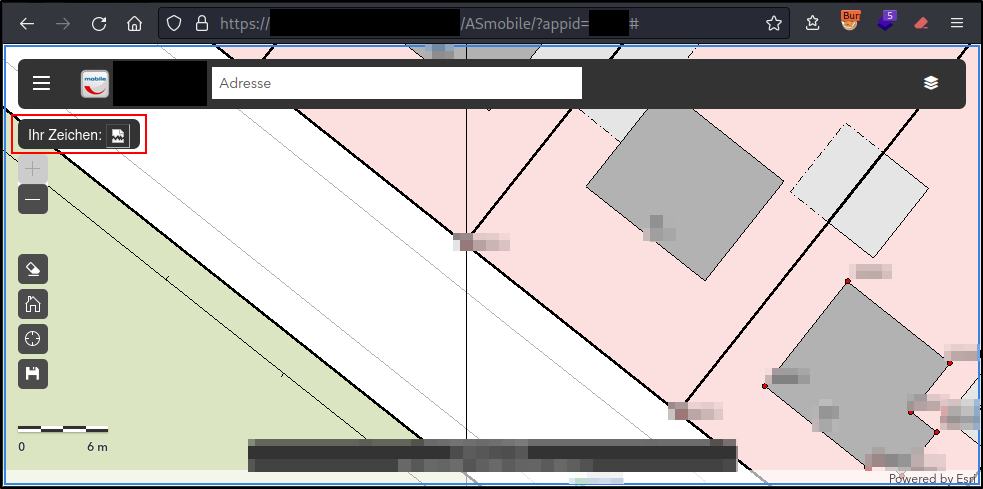
A user's business reference can be edited by the user through the "ASMobile" web interface, when being logged in. For demonstration purposes, an image HTML tag can be inserted in the reference, which, when causing an error, executes a JavaScript alert. When adding such a
payload to the business reference and exiting the text field, the JavaScript alert will be executed, as can be seen in figure 4 below: [04_stored_xss_2_alert.png] Rechecking the business reference
after exiting the alert shows that the malicious image tag was rendered inside the page, as shown in figure 5 below: [05_stored_xss_2_rendered.png] When placing orders through the web interface, the
user's business reference will also be included. After the order is placed, it will be listed in the administrative OrderAdministration portal and the malicious JavaScript code will be executed in a
high privileged browser of the victim, when it visits that order. Vulnerable / tested versions: ----------------------------- The following version has been tested which was the latest version
available at the time of the test: * WebOrderSystem (7.0.8.6) Different software components, including WebOrderSystem, GIS Portal and multiple 3A Web components, were installed on the tested system.
The vulnerabilities were associated with the WebOrderSystem. The vendor did not provide further information which exact products or versions are affected. Vendor contact timeline:
------------------------ 2025-01-30: Contacting vendor through 3a-lm-support@xxxxxxxxxxxx Received automatic response from support ticket system. Later received response from support employee, asking
on whose behalf we work. 2025-01-31: Explaining context to support contact and asking for correct security contact to send the advisory. Support contact informs that the customer already provided the
vulnerability information in the form of a report excerpt. Pointing out the Responsible Disclosure process to the support contact again. 2025-02-14: Asking for updates and the planned next steps to
remediate the vulnerabilities. 2025-02-18: Vendor provides detailed evaluation and opinion on all instances. The vendor sees the instances described in this advisory as non-critical, as access to the
CustomerAdministration portal (KundenManager) should generally be restricted to a small user group and the site is recommended to be restricted to Intranet access. However, both instances are planned
to be addressed in a separate hardening of the KundenManager during further development of the VertiGIS product "LM Explorer" (successor
            product of "3A Web").
2025-02-19: Clarifying the opinion regarding the criticality of the instances
to the
            vendor and asking for an estimated timeline regarding the hardening
            of the KundenManager.
2025-02-24: Vendor gives further insights and opinion on the instances.
2025-02-26: Adding a new vulnerability to this advisory, which was previously
            considered a "self-XSS" but confirmed by the vendor to be
exploitable in
            another component.
            Asking vendor to confirm the names of the affected software
components.
            Also asking for a timeline for when all instances are planned to be
            remediated.
            Vendor confirms that both, the KundenManager und AuftragsManager,
are part
            of the WebOrderSystem installation.
            Vendor cannot give an estimated timeline yet, on when the instances
will
            be remediated.
2025-02-28: Asking vendor to confirm existing contact for sending updated
            security advisory.
2025-03-12: Vendor confirms existing communication channel.
            Sending updated security advisory.
2025-05-21: Asking for a status update.
2025-05-22: Vendor still can not provide an estimated timeline for remediation.
            The instances are planned to be addressed with the release of "LM
Explorer".
2026-03-26: Asking for a status update.
2026-03-27: Reserving CVEs.
2026-04-13: Vendor provides general security announcement links for "3A" and
"VertiGIS LM"
            that do not include information on any of the vulnerabilities from
this advisory.
            Asking vendor to explain the relationship between the
"WebOrderSystem" component
            and "3A Web" and if this component is relevant in "LM Explorer" at
all, as there
            are no separate announcements for "WebOrderSystem".
            No response.
2026-10-15: Informing vendor that our advisory will be published the following
week;
            No response
2026-10-23: Release of security advisory.


Solution:
---------
The vendor did not communicate a patch for the identified vulnerabilities in
VertiGIS "WebOrderSystem" and told us that "LM Explorer" will incorporate the
fixes. Version numbers were not provided nor when the fixes were implemented.
Contact the vendor fur further information regarding fixes or hardending
measures.

Furthermore, the vendor recommends following their product announcements:
https://support.vertigis.com/hc/de/sections/4403356759570-Ank%C3%BCndigungen
https://support.vertigis.com/hc/de/sections/23916902893458-Ank%C3%BCndigungen
https://support.vertigis.com/hc/de/sections/26551407185810-Ank%C3%BCndigungen


Workaround:
-----------
- CVE-2026-4950: None
- CVE-2026-4951: None
- CVE-2026-4952: In the current version (as of 2025-02-24) it is already
possible to
                 define an optional regular expression for the business
reference. This
                 can also act as an input validation for Cross-Site Scripting.


Advisory URL:
-------------
https://sec-consult.com/vulnerability-lab/


~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~

SEC Consult Vulnerability Lab
An integrated part of SEC Consult, an Atos business
Europe | Asia

About SEC Consult Vulnerability Lab
The SEC Consult Vulnerability Lab is an integrated part of SEC Consult, an
Atos business. It ensures the continued knowledge gain of SEC Consult in the
field of network and application security to stay ahead of the attacker. The
SEC Consult Vulnerability Lab supports high-quality penetration testing and
the evaluation of new offensive and defensive technologies for our customers.
Hence our customers obtain the most current information about vulnerabilities
and valid recommendation about the risk profile of new technologies.

~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~
Interested to work with the experts of SEC Consult?
Send us your applicationhttps://sec-consult.com/career/

Interested in improving your cyber security with the experts of SEC Consult?
Contact our local officeshttps://sec-consult.com/contact/
~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~

Mail: security-research at sec-consult dot com
Web:https://www.sec-consult.com
Blog:https://blog.sec-consult.com
X:https://x.com/sec_consult

EOF Kai Zimmermann / @2026
Attachment:
01_stored_xss_01.png
Description: PNG image
Attachment:
02_stored_xss_02.png
Description: PNG image
Attachment:
03_reflected_xss.png
Description: PNG image
Attachment:
04_stored_xss_2_alert.png
Description: PNG image
Attachment:
05_stored_xss_2_rendered.png
Description: PNG image
Attachment:
smime.p7s
Description: S/MIME Cryptographic Signature
_______________________________________________
Sent through the Full Disclosure mailing list
https://nmap.org/mailman/listinfo/fulldisclosure
Web Archives & RSS: https://seclists.org/fulldisclosure/